Sheet 01 / 08
GHOST PROTOCOL
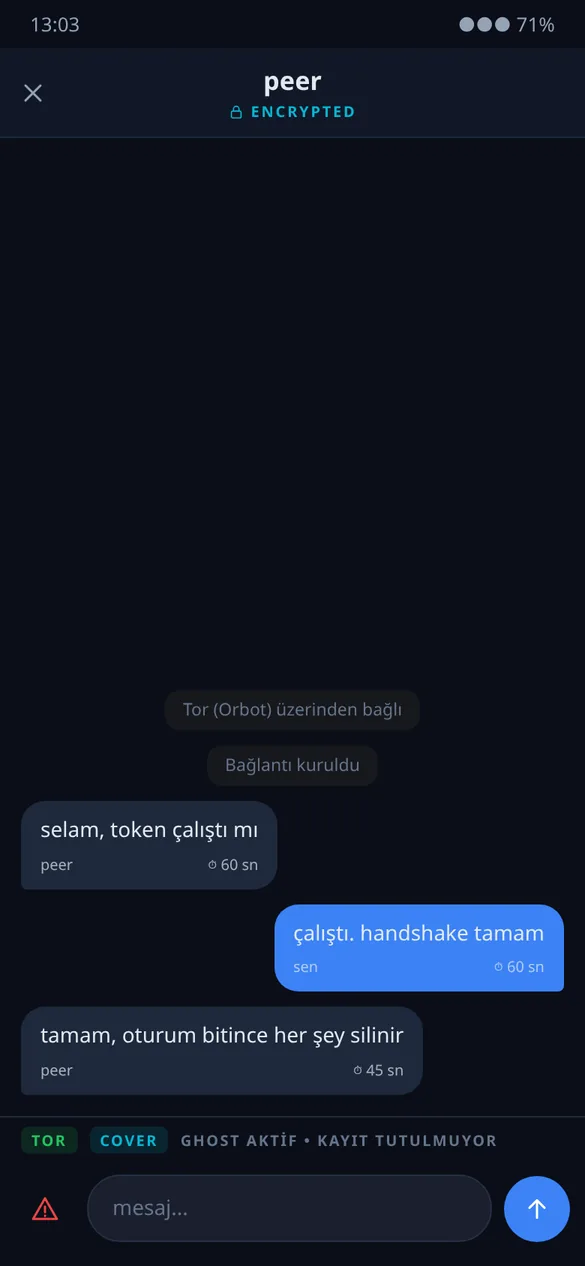
End-to-end encrypted, anonymous, real-time messaging system. Traffic goes through Tor, messages live only in memory and nothing is left behind when the session ends.
- Subject
- Security
- Platform
- Windows · Linux · macOS · Android
- Version
- 1.1.0
- Source
- Closed source
- Date
- 2025–2026
- Status
- On hold
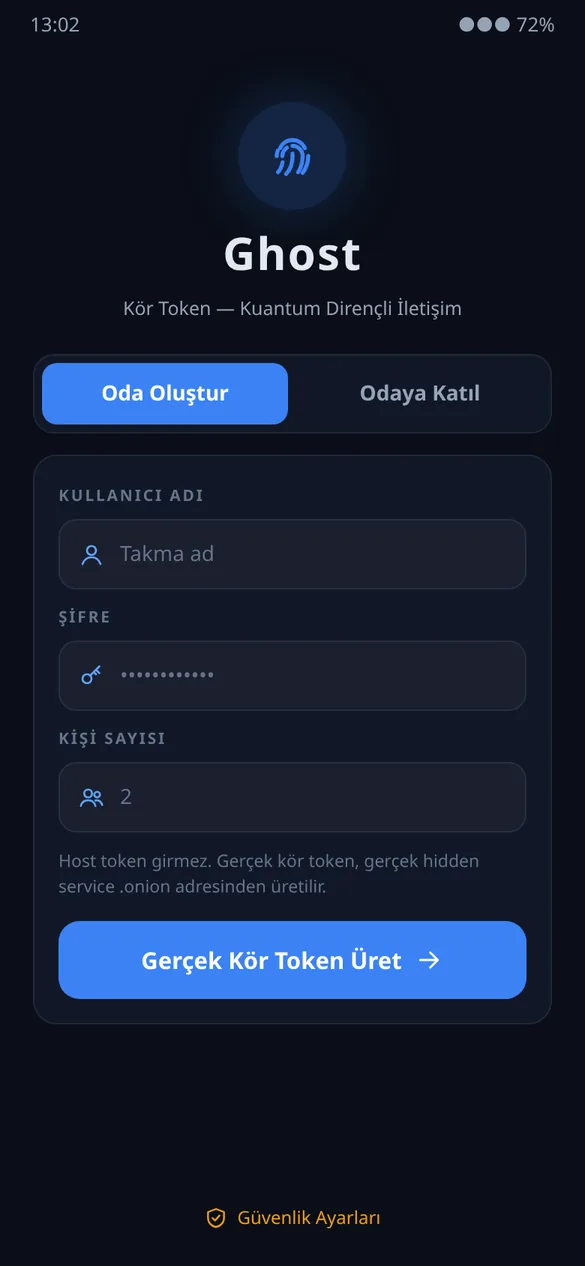
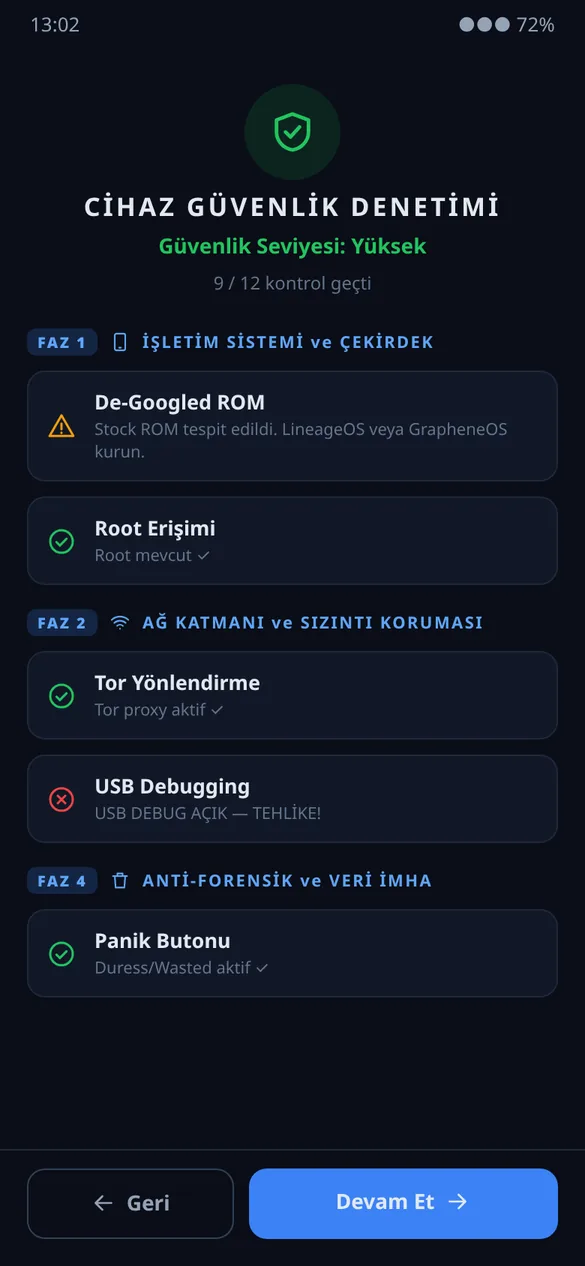
01ViewsRedrawn from Compose code · sample data
02Schema and notes
- Key exchange uses a hybrid X25519 + Kyber-1024 handshake.
- No server; connections go through Tor using a blind token.
- Messages are kept only in RAM; memory is locked and core dumps are disabled.
- No logs; a 7-pass wipe runs on shutdown.
- Core in Rust and Tokio; the Android client binds to the core through JNI.
03Parts list5 parts
| Item | Part | Description |
|---|---|---|
| 01 | Crypto layer | Hybrid X25519 + Kyber-1024 handshake, session keys |
| 02 | Network layer | Routing over Tor, blind-token connection |
| 03 | Memory protection | RAM encryption, memory locking, core dump prevention |
| 04 | Trace wiping | No logs, 7-pass wipe on shutdown |
| 05 | Android client | JNI bridge to ghost_core |
—End of sheetdrawn by MUHAMMEDPYZ